Mini AI SOC
A full security operations centre in a single Docker Compose stack.
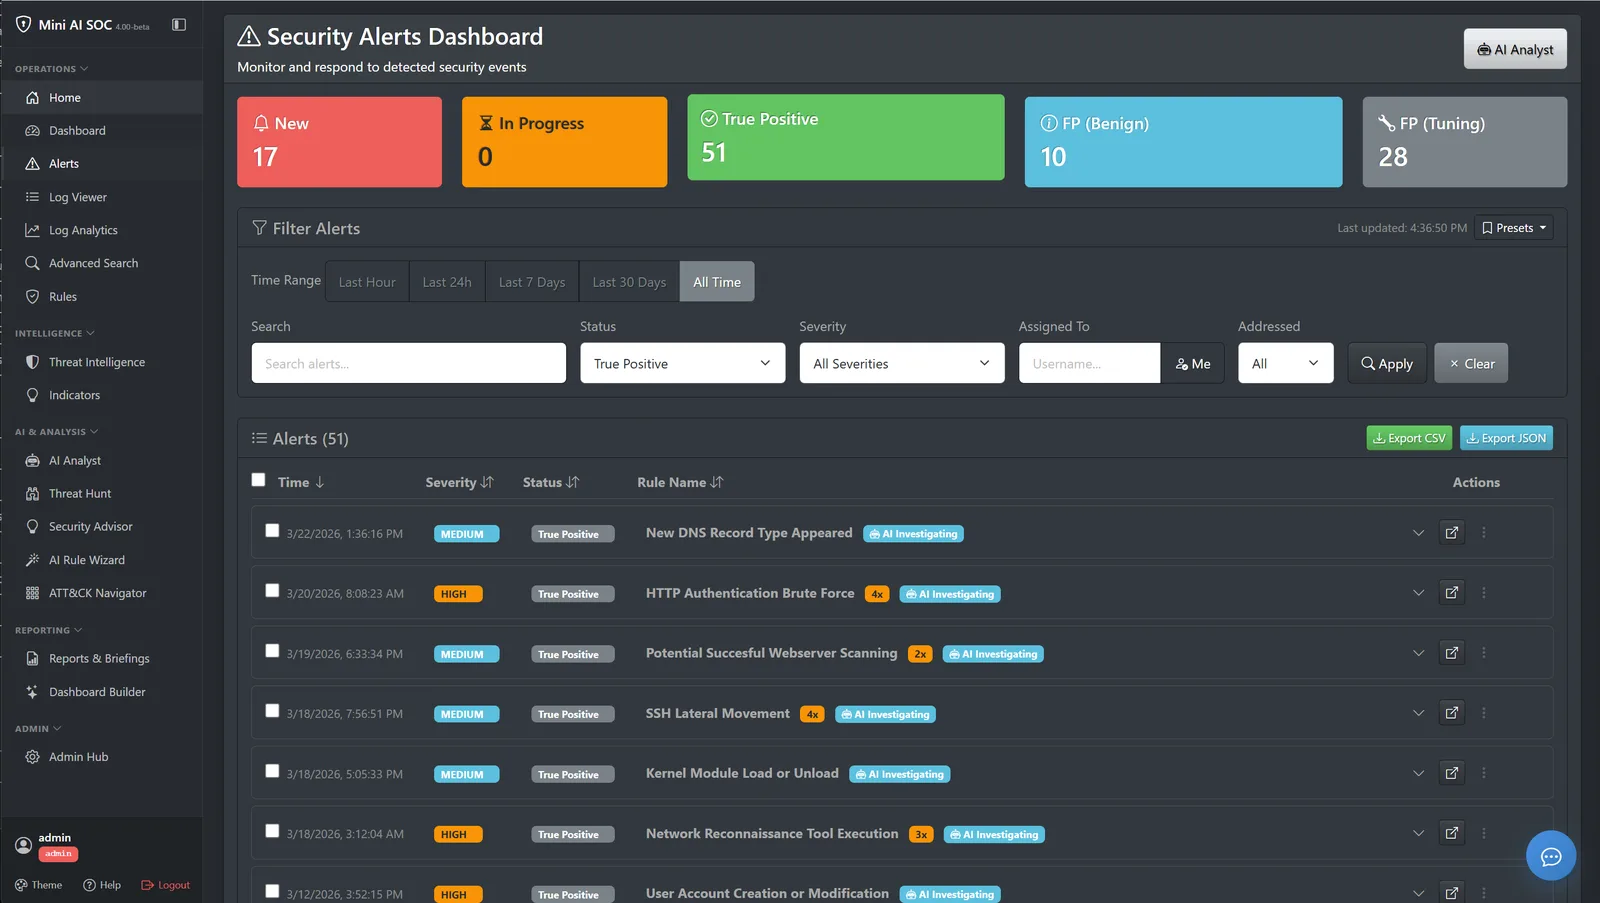
Most small companies will never have a SOC. They can’t staff one around the clock and can’t pay for the tooling. Mini AI SOC is my attempt to fit the whole thing, SIEM, threat intelligence, SOAR, network IDS, a TLS-inspecting proxy and a honeypot, into one stack that starts with a single command.
An AI analyst works every alert with tool calls before a person looks at it. It also writes detection rules from a plain-English description, tunes the noisy ones, and points out which attacks your rule set doesn’t cover yet. The same platform runs as a managed service for small and mid-size businesses, with human analysts available on top.
In the box
- 170+ detection rules, mapped to MITRE ATT&CK
- 34 log formats, normalised to Elastic Common Schema
- Microsoft 365, Entra ID and Defender, across tenants
- 35 threat-intel feed presets, TAXII and STIX
- Suricata IDS, Squid with ClamAV, Cowrie honeypot
- Endpoint agents for Windows and macOS
- SOAR playbooks that fire on new alerts